Who actually controls the cloud?
Keeping data in Frankfurt means little if someone outside your jurisdiction controls the keys needed to decrypt it.
Kubernetes and the infrastructure beneath it often operate as separate systems. I'm building the control plane that connects them into a working cloud platform.
Keeping data in Frankfurt means little if someone outside your jurisdiction controls the keys needed to decrypt it.
Kubernetes expects a node. An infrastructure platform provides a machine, network interfaces, volumes and routes. Making those resources work together as one Kubernetes node is the hard part.
A missing response doesn't tell you whether the operation failed or completed successfully. Retry a machine creation request without checking, and you might end up with two machines instead of one.
Writing
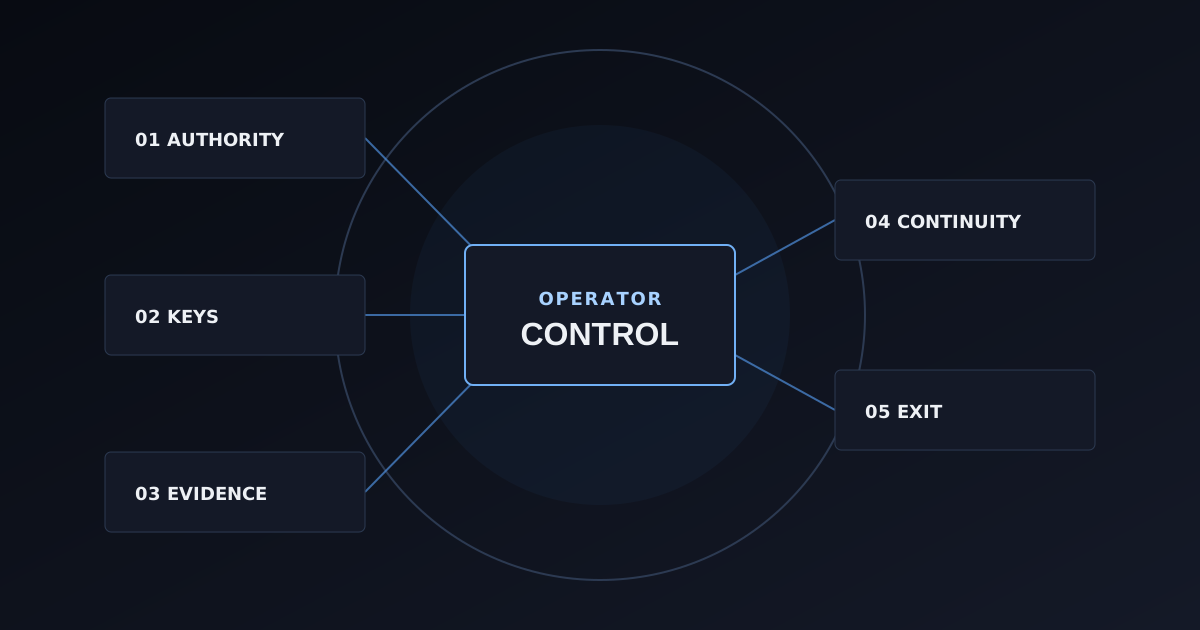
Data residency tells you where bytes are stored. It does not tell you who controls identity, keys, audit evidence and recovery, or whether the operator can move the platform elsewhere.
Speaking